

GHSA-fj52-5g4h-gmq8 json
pyLoad's Session Not Invalidated After Permission Changes
published 7mo ago modified 7mo ago
- cvss
- —
- not scored
- cisa kev
- Not listed
- not in CISA's catalog
- epss
- —
- no score, EPSS covers CVEs only
- public exploits
- 0
- none known
Summary
### Summary The `pyload` application does not properly invalidate or modify sessions upon changes made to a user's permissions.
### Details Whenever an administrator changes the permissions a specific account has, they do not expect that account still being able to access data that their new permissions do not allow. This is not the case for the `pyload` application, as a user with a valid session can still perform the actions.
### PoC Take a user with all the permissions, as shown below. 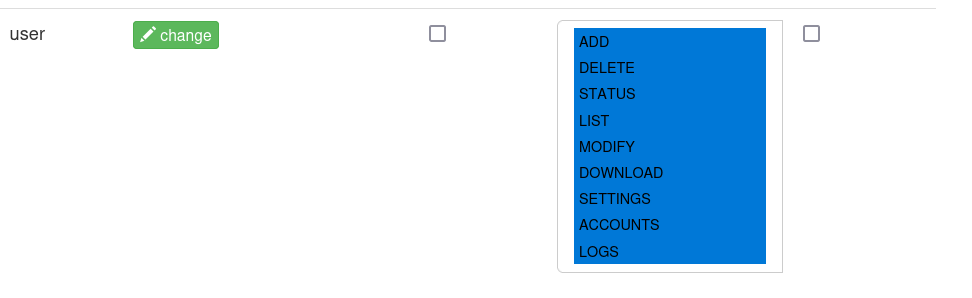
We now log in as this user. 
Let us now take away all the permissions. 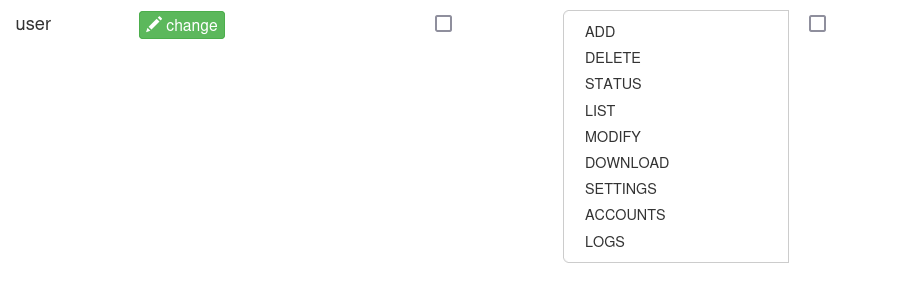
The logged in session can still be used to access everything in the application. 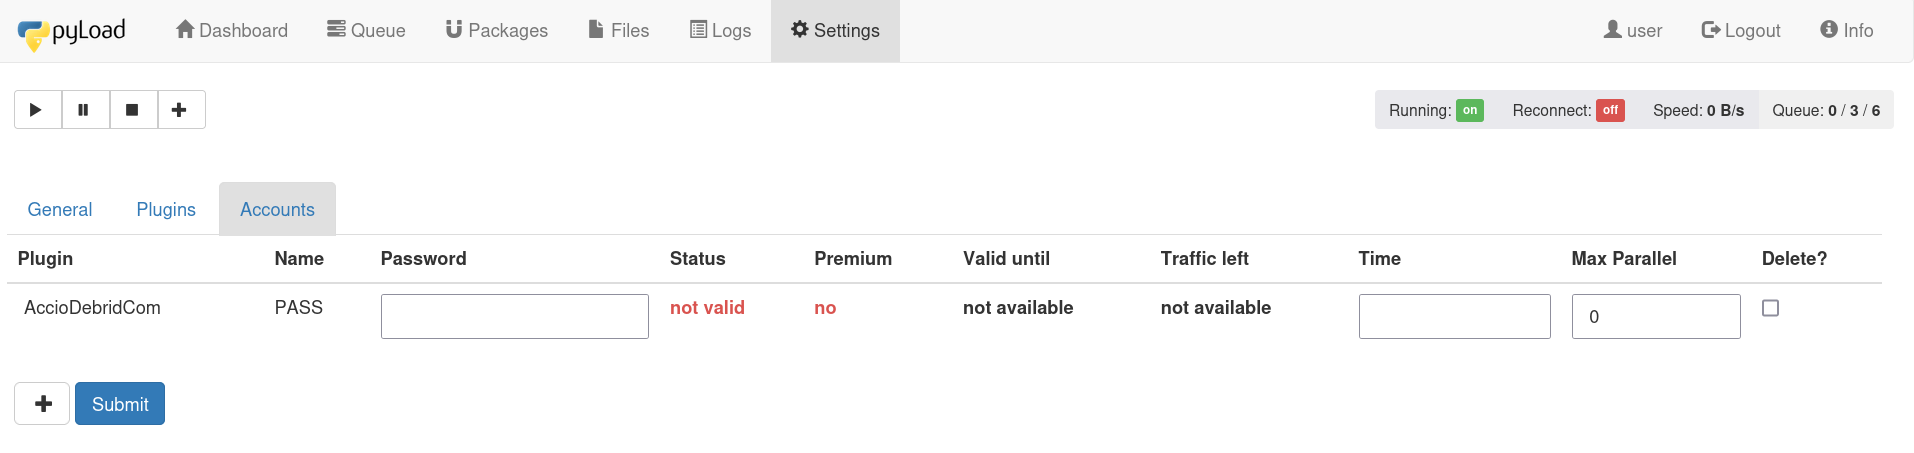
### Impact Should permissions be taken away, then the user is expected not to be able to execute the actions belonging to those actions anymore.
Patch / fix
Is GHSA-fj52-5g4h-gmq8 in your dependencies? Fencer shows which of your repositories are affected as soon as an advisory lands, and opens the fix as a pull request.
Check with FencerAffected packages
| ecosystem | package | affected | fixed in |
|---|---|---|---|
| pypi | pyload-ng | <=0.5.0b3.dev97 |
no fix listed |
Classification
- Weakness
-
- CWE-613 DEPRECATED: Insufficient Session Expiration
References
Sources
- GitHub Advisory GHSA-fj52-5g4h-gmq8
Fencer Intel keeps one entry per vulnerability: the CVE id wins, then GHSA, and records that alias each other are merged, except that two CVEs always keep separate entries. The same data is available as JSON.