

- cvss
- 3.3
- version 3.1, GitHub
- cisa kev
- Not listed
- not in CISA's catalog
- epss
- —
- no score, EPSS covers CVEs only
- public exploits
- 0
- none known
Summary
### Summary when jadx parses a resource file, there is an escape problem with the style file, which can overwrite other files in the directory when saving the decompile result.
Although I don't think this vulnerability realizes path traversal in the true sense of the word , I reported it anyway
### Details
I see that getResAlias does something with the filename.
```java private String getResAlias(int resRef, String origKeyName, @Nullable FieldNode constField) { ```
but type style will return the original filename directly.
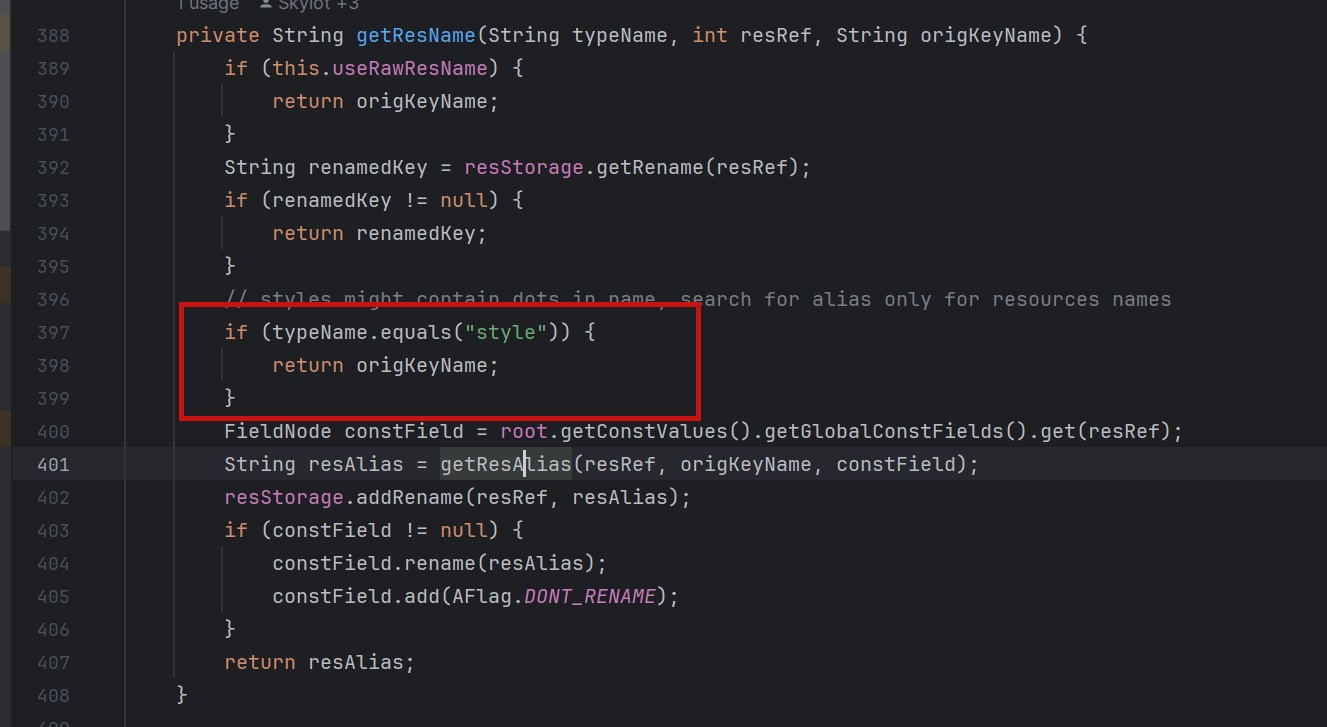 so our goal is to take a malicious file that was originally of type raw, modify its type to style, trick jadx into
#### step1
create an android project using androidstudio and create a raw folder with the name attack_file_sayhiiiiiiiiiiiii, it doesn't matter what the content is!
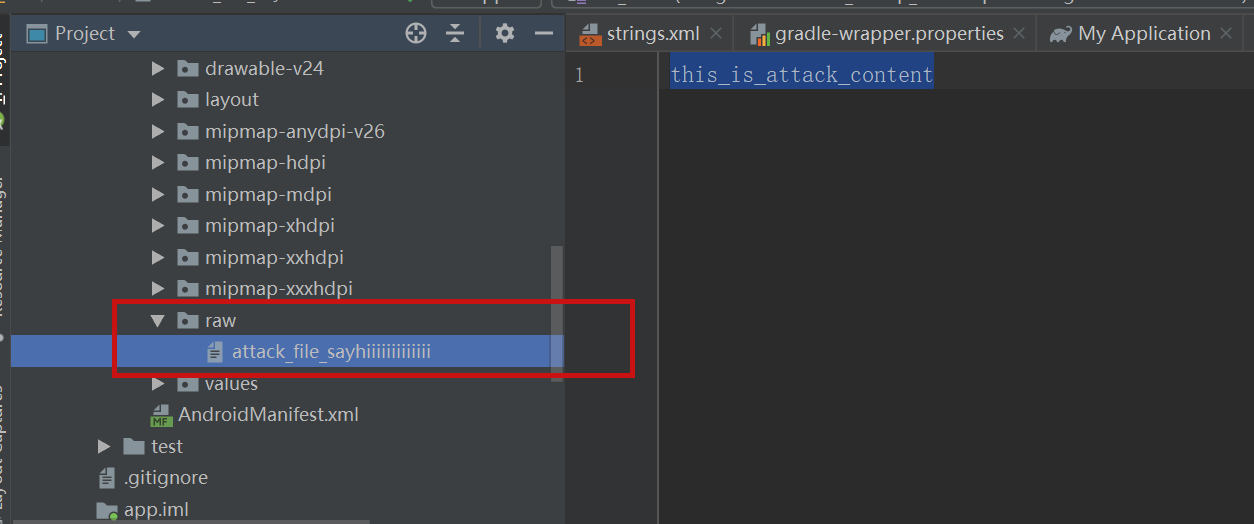 generate an initial APK
#### step2
extract this initial APK using ZIP software to get resources.arsc
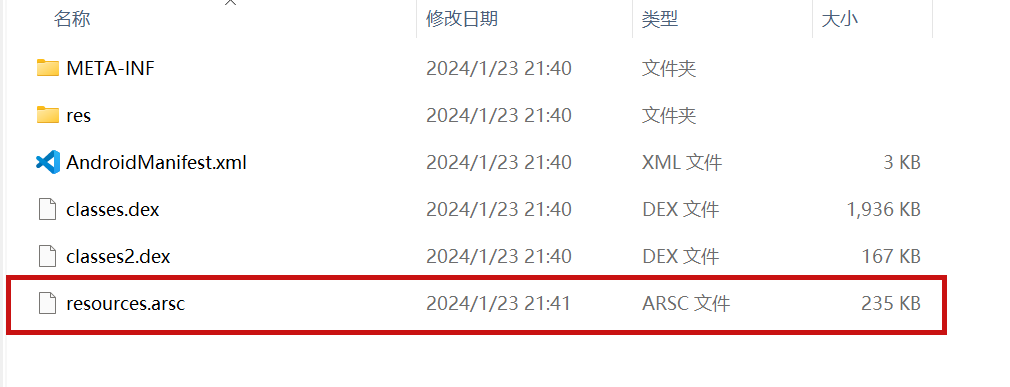 drop resources.arsc into 010editor
#### step3
search for the previous filename attack_file_sayhiiiiiiiiiiiii , two will appear here, we choose the second one
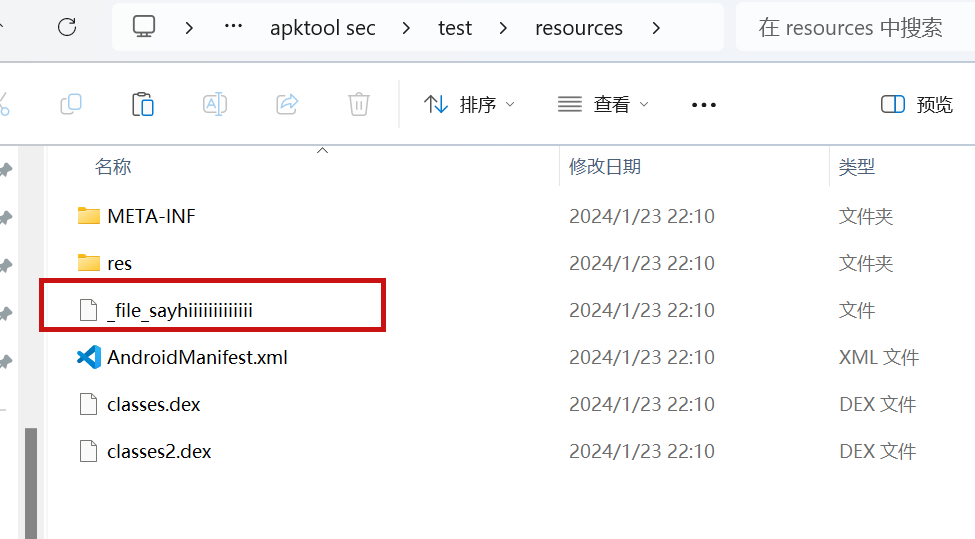
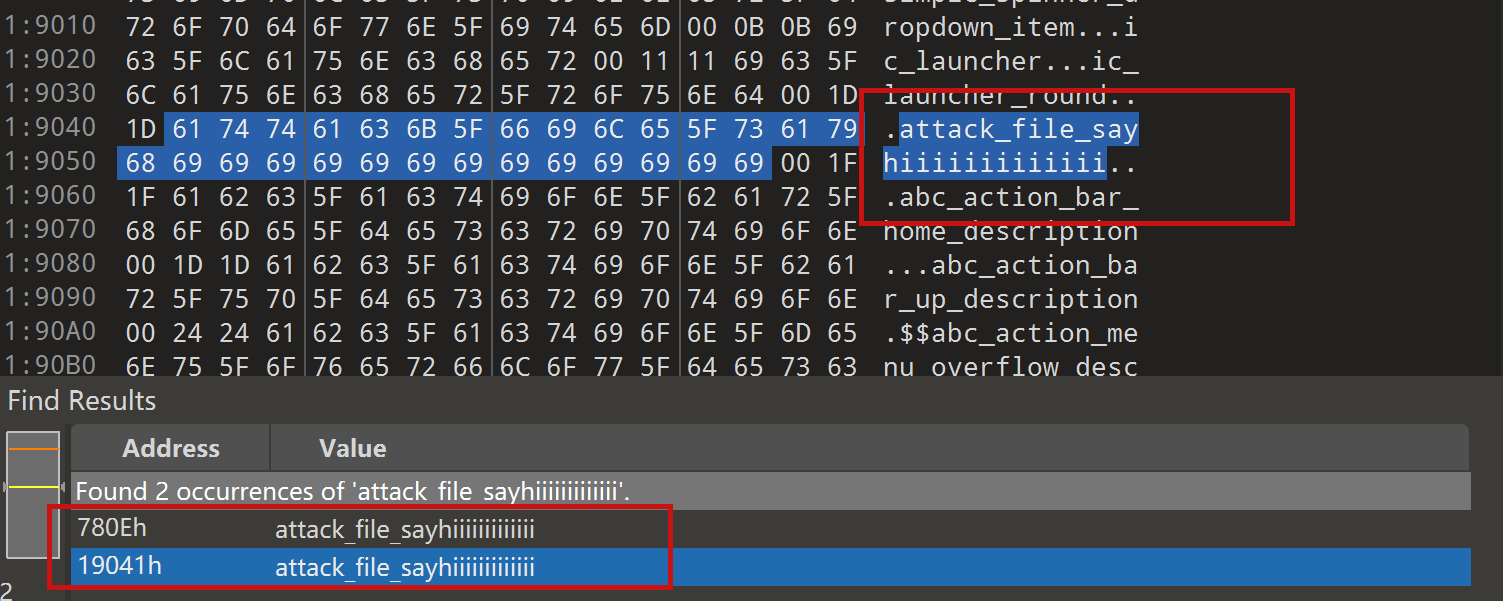 let's change the name of the file here. I'll change it to ../../_file_sayhiiiiiiiiiiiii
note that you can only overwrite files in the folder where the decompile was saved.
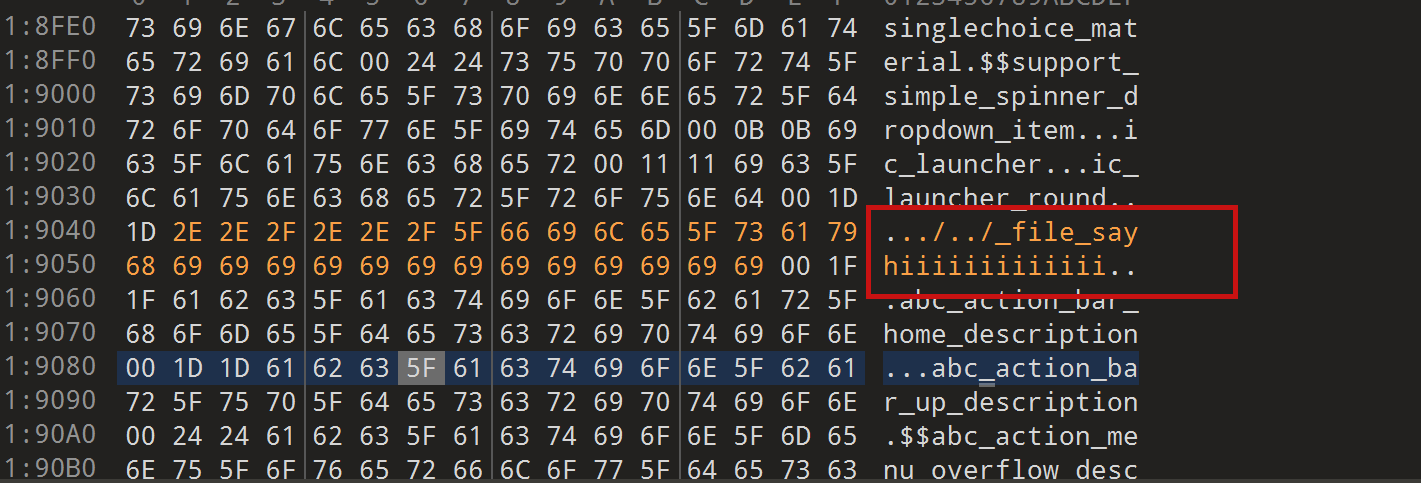 #### step4 change the type of this file to style
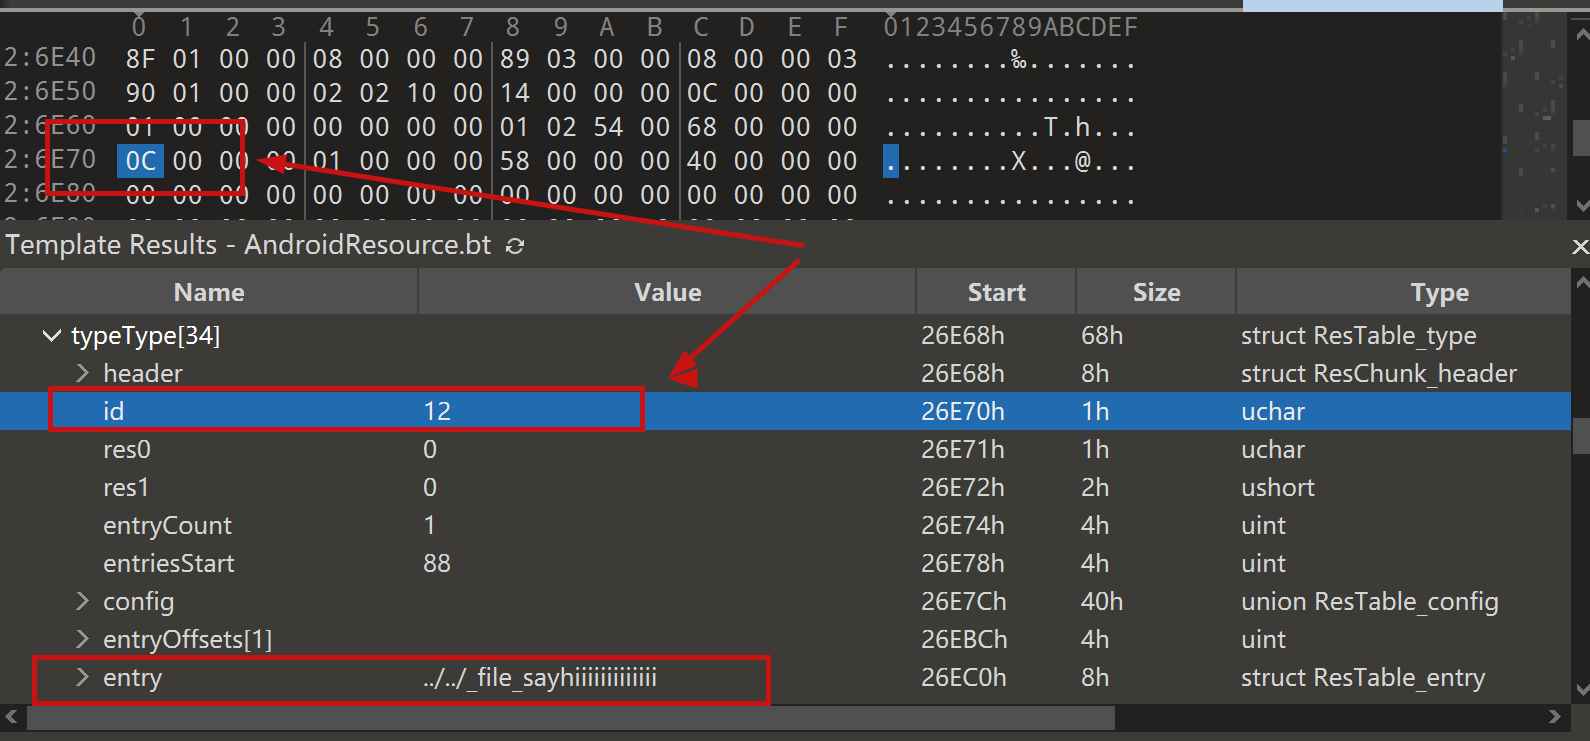 modified to 0E
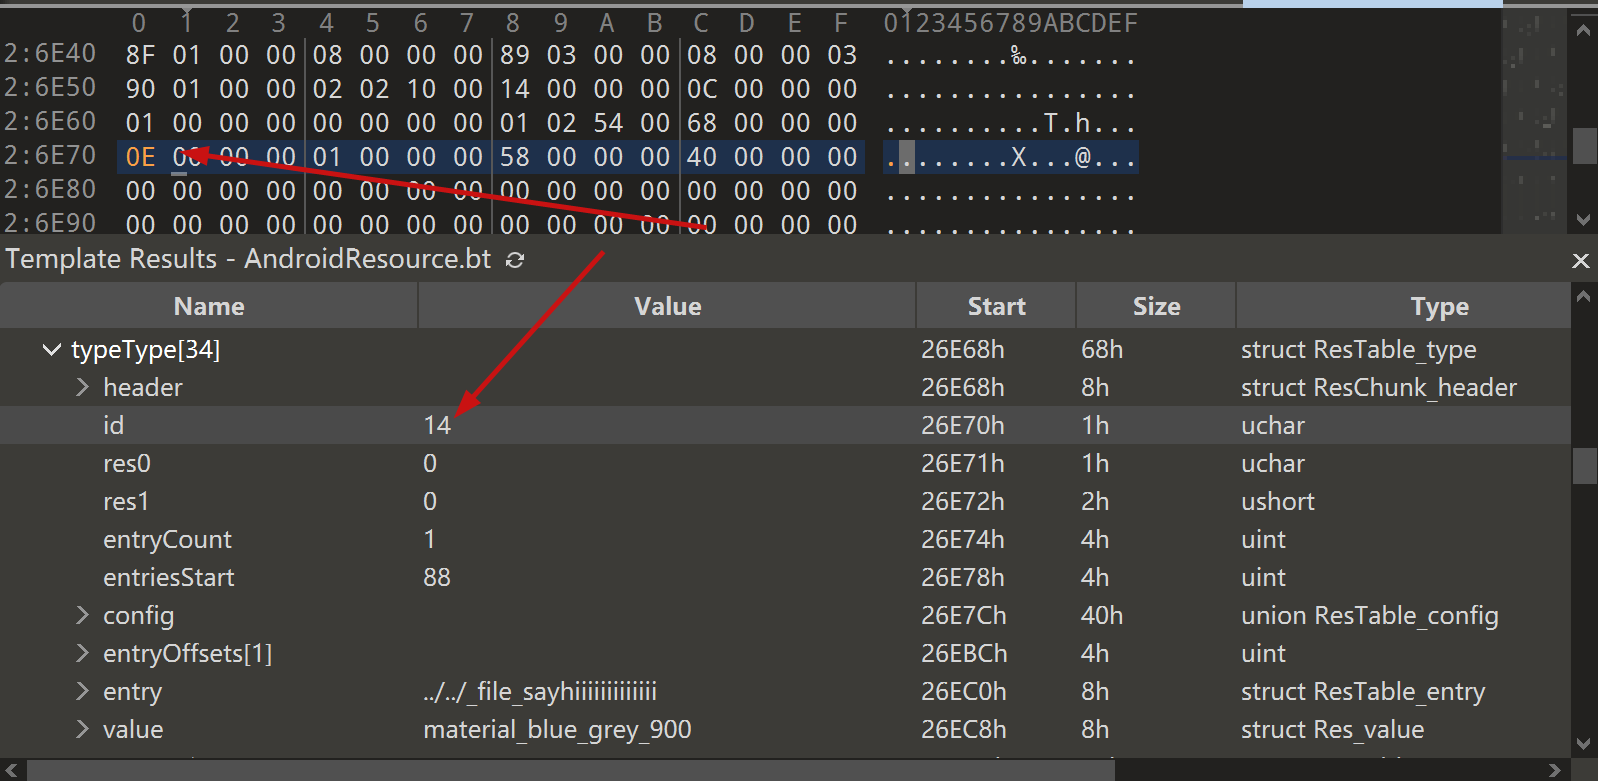 #### step5
After saving, re-compress the whole folder into a zip, then change the extension to APK.
open it with JADX and you can see that it has been changed to a style type.
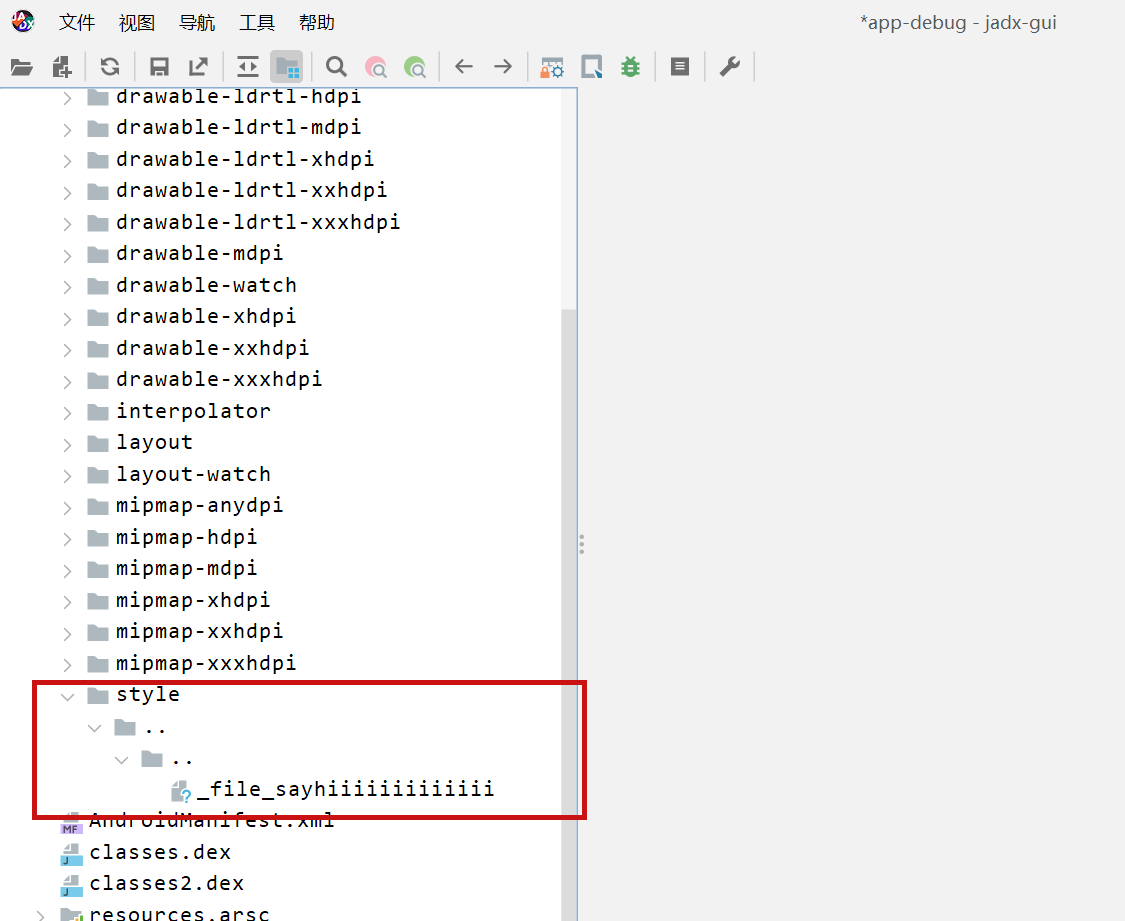 click save all
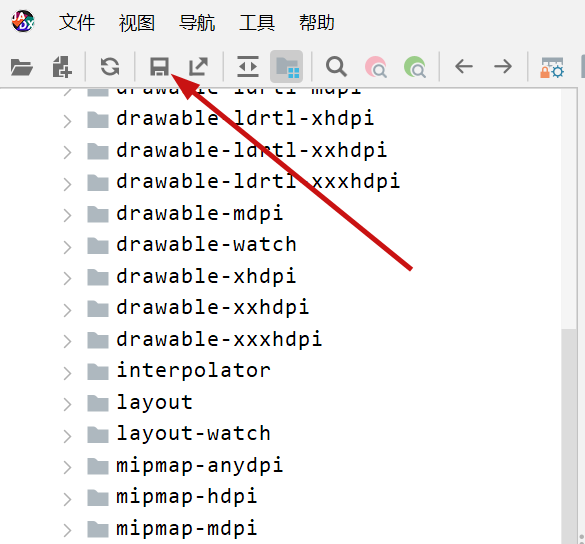 you can see the file escaping.
 so we can also construct a
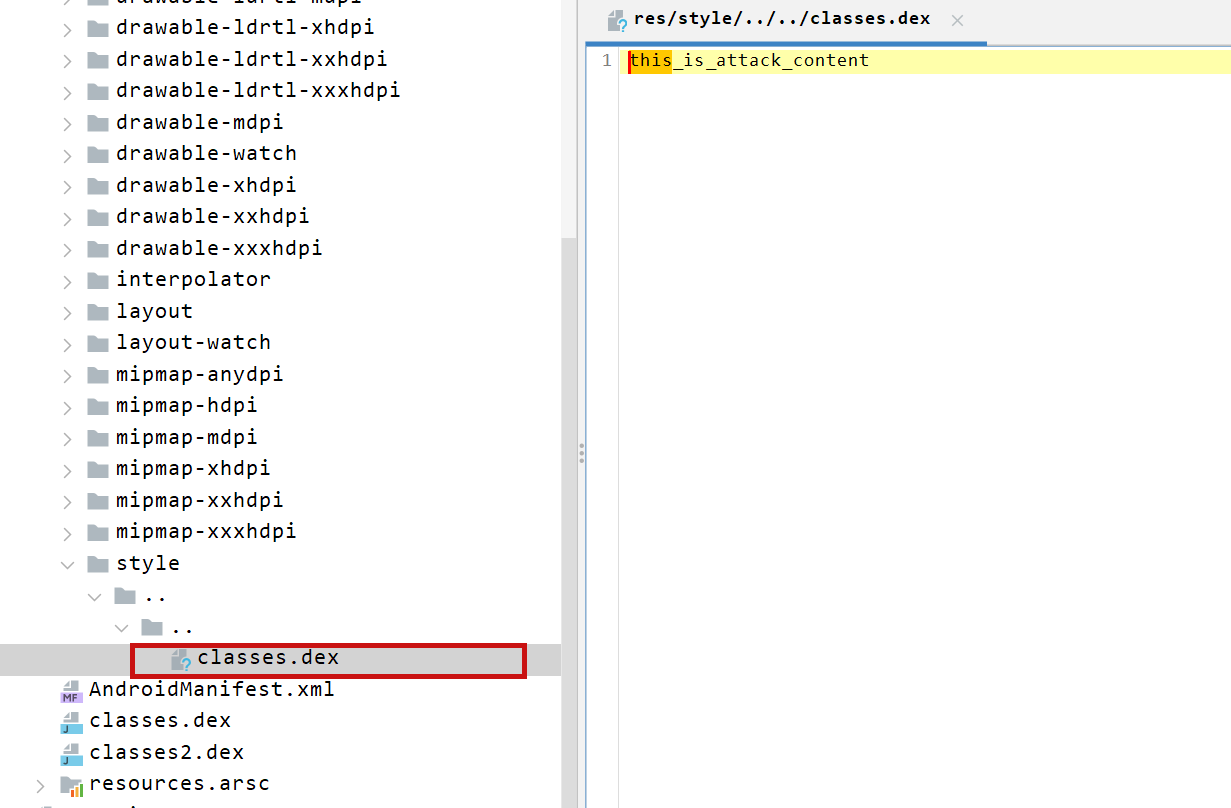 so the classes.dex file is also replaced here
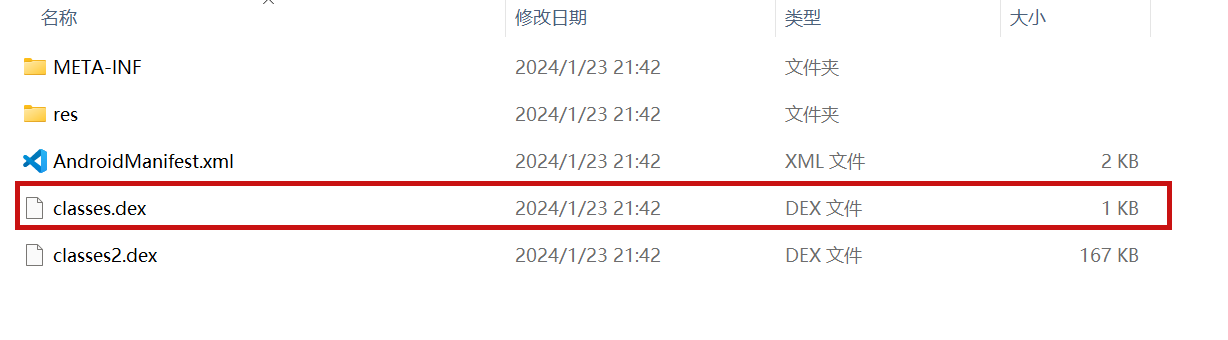
### PoC the details above have been written
### Impact latest version
Patch / fix
Is GHSA-hvp5-5x4f-33fq in your dependencies? Fencer shows which of your repositories are affected as soon as an advisory lands, and opens the fix as a pull request.
Check with FencerCVSS scores
| assigned by | version | score | vector |
|---|---|---|---|
| GitHub | 3.1 | 3.3 | CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N |
Affected packages
| ecosystem | package | affected | fixed in |
|---|---|---|---|
| maven | io.github.skylot:jadx-core | <1.5.0 |
1.5.0 |
Classification
- Weakness
-
- CWE-22 Improper Limitation of a Pathname to a Restricted Directory
References
Sources
- GitHub Advisory GHSA-hvp5-5x4f-33fq
Fencer Intel keeps one entry per vulnerability: the CVE id wins, then GHSA, and records that alias each other are merged, except that two CVEs always keep separate entries. The same data is available as JSON.